Most cybersecurity startups sell shields. Twenty sells the sword, and investors just valued that at $1bn. The company, which describes itself as America’s first venture-backed cyber warfare firm, has raised a $100mn Series B led by Accel, Axios reporte…
The figure that reframes the problem is a share, not a sum. In more than half the countries Interpol surveyed for its latest Asia and South Pacific cyber-threat assessment, cybercrime now accounts for around 30% of all crime recorded nationally. That i…
A cyber-extortion group calling itself FulcrumSec said on Monday that it had stolen roughly 1.3 terabytes of data from Novo Nordisk, the Danish maker of the weight-loss drugs Wegovy and Ozempic, and had demanded $25 million to keep it private. Novo Nor…
Security researchers at Zimperium’s zLabs have documented a new Android banking trojan that targets 217 banking and cryptocurrency applications and carries 137 remote commands, giving an operator near-total control of an infected phone. The malware, wh…
One of the largest open-source package repositories just spent a weekend cleaning up after a malware campaign that did not break into anything. It did not need to. Attackers seized control of more than 1,500 packages in the Arch User Repository, or AUR…
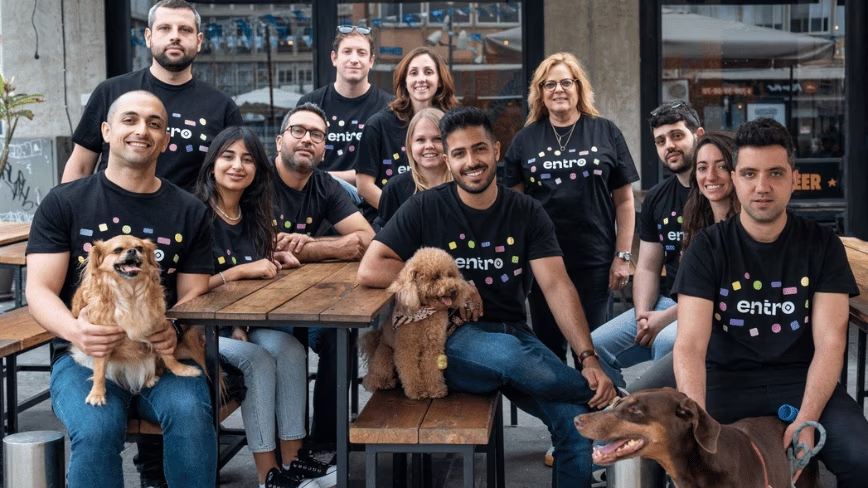
The race to secure non-human identities just produced its second deal of the day. SailPoint, the Austin-based identity-security giant, said it plans to buy Entro, a Tel Aviv startup that finds and protects the credentials, keys and machine accounts tha…
1Password is buying its way into the agentic enterprise. The Toronto identity-security company said on Monday it has acquired Apono, an Israeli startup that decides, in real time, what every human, machine and AI agent is allowed to touch inside a comp…
SoftBank and OpenAI are moving into cyber defence. The two said on Tuesday they are launching “Patching as a Service,” a security product built on OpenAI’s technology, to shield the companies behind Japan’s critical infrastructure from a rising wave of…
The Canadian government introduced legislation on Monday to overhaul the country’s private-sector privacy laws, including new restrictions on businesses that use personal data to charge individual consumers higher prices. Bill C-36, the Protecting Priv…
A China-linked espionage group spent more than a year inside North American medical, academic, and military research networks, stealing sensitive data and defence email. The attackers got in through a backdoor on REDCap research servers. The exfiltrati…