Every time a Mastercard gets tapped, the network has less than a tenth of a second to judge how likely the purchase is to be fraudulent. It made that call across 175 billion transactions last year. Now the buyer on the other side of that judgment is starting to change, and Greg Ulrich, the company’s chief AI and data officer, spelled out the consequence for the VB Transform 2026 audience in Menlo Park on July 14. “We’ve built a bunch of risk rules over time that were intended to stop a bot from transacting,” Ulrich said. “Now we need to enable the bot to transact, so that requires a change to our risk framework and our risk rules.”
Ulrich joined Mastercard eleven years ago when an analytics company he worked at was acquired, and said trust struck him from day one on the job. “It’s what enables a merchant that’s never met you to accept payment and ensure that they’re going to get paid. It’s what enables you as a consumer to transact and ensure that things are going to work out in a trusted, secure way. And if something goes wrong, there’s a safe and secure path for a dispute and to resolve this,” he said.
175 billion transactions, scored in under 100 milliseconds
He took the audience inside each of those calls. “When you tap your Mastercard to pay for a product or service, we’re providing a score to that transaction,” he said. “We have under 100 milliseconds to look at that and give a score from zero to 999 about how likely is that to be fraudulent or real. And we pass that on to the issuing bank.”
Generative AI widened what that score can see. “Because we have new technology, we can bring in more data, we can bring in more context, and now we’re finding that we can identify 300, 400% more fraudulent transactions at those high-risk bands,” Ulrich said, without adding friction or false positives for consumers. The company’s Safety Net system has stopped more than 70 billion fraudulent transactions, he told the audience, and Mastercard is building its own transformer model on its transaction data as a foundation for new safety, security, and personalization solutions. VentureBeat’s Beyond the Pilot podcast took that production fraud stack apart in detail earlier this year.
A third of the services business already runs on AI
The business stakes reach past fraud. About 40% of Mastercard’s company is now based on services, Ulrich said, including marketing services; fraud, safety and security; and business intelligence. “A third of those are predicated on AI, and those are growing at a much faster clip than everything else,” he said.
One line he returned to all session went further. “What’s going to enable AI to continue to scale is not the capabilities of the agents, it’s how much we trust those agents to do on our behalf as a consumer, as a business, as a financial institution, or otherwise,” he said.
Five layers stand between agents and the network
Agentic commerce changes the object being secured. “Instead of a single atomic transaction where I say go buy something, I’m effectively delegating authority, or a consumer’s delegating authority, a business is delegating authority,” Ulrich said. “And when that happens, it’s a much more complicated transaction.” Trust, in turn, has a precondition. “The only way it’s going to work with trust is if we can identify what was the intent, what are the behaviors, what are the constraints that were intended in that transaction.”
Ulrich walked through five layers Mastercard has built against that problem. Identity comes first. “I want to make sure I can understand not just who the consumer is, but who the agent is, that I combine them together and that I have KYA or know your agent, that I’m validating that it’s legitimate technology, that it’s a legitimate agent,” he said. “We can register it into our system.”
Verifiable intent settles the “wrong-Nikes” problem
Verifiable intent is second, a tamper-proof cryptographic record of the original instructions that travels with the transaction. “If you’ve asked for Nike black Nikes in size 12, but you got them on a final sale and they’re not returnable and that wasn’t in your instruction, there’s a way to look at that in an objective and clear way on the back end,” he explained.
Controls form the third layer, defining which merchants an agent can buy from, at what limit, and under what constraints. Execution runs through Mastercard Agent Pay, which carries “the tokenization, authentication, the acceptance framework embedded within it” and has launched with Microsoft, OpenAI, Google, and others, Ulrich said. Intelligence is the fifth layer, spanning risk rules, insight tokens that grant “consented or permissioned access to insights” for personalized recommendations, and monitoring through Recorded Future to identify threat actors in the system.
The bigger prize is a procurement agent with a budget
Consumer purchases are where agentic commerce started. Ulrich pointed the room past them, to business-to-business procurement as the larger opportunity. His example was a manufacturer that wants an always-on assembly line, with an agent that manages inventory levels, tracks when stock runs low, replenishes automatically, and understands the budget and the approved suppliers. “When you can start enabling that, you require those same five layers for that type of transaction,” he said.
Making it work across companies multiplies the parties that have to trust each other. “You need clear standards for identity, you need clear standards for intent, you need these to work across. You’re gonna have a procurement agent, a supplier agent, a banking agent. They’re all gonna need to communicate to enable this to happen in an autonomous way, and that’s gonna require really scaled trust infrastructure.”
Powerful new models, same security motion
Mastercard sat in the early wave of Project Glasswing with Anthropic’s Mythos model, and worked with OpenAI’s GPT-5.5-Cyber, he said. “What we’ve seen from both of those is incredibly powerful models finding new vulnerabilities in the ecosystem that were difficult to detect previously, but it’s really a new tool as opposed to a new motion,” Ulrich said.
Inside the company, the chief security officer leads that work. A dedicated team has prioritized the most critical assets, runs them through the models routinely, tracks findings by high, medium, and low severity, and uses the same technology to handle patches. Ulrich said the approach has already been extended out, and that Mastercard is working to make the same architecture and patching available to others as well.
What Mastercard would build differently after 14 months
“The guardrails, the security, all this stuff has to be embedded at the front end. These can’t be things that we’re adding on at the back end. That’s lesson one. Lesson two is you have to be operating for scale, and the other one is around observability and accountability matter as much as the intelligence,” Ulrich said, counting off what building inside Mastercard taught the team. The company built what he described as an agentic factory, an operating system with the compliance, the observability, and the guardrails built in rather than bolted on per agent. Model drift, once tracked manually by dedicated teams, is now automated into that factory.
Asked by an audience member about the gotchas, Ulrich did not soften the pilot-to-production trap. “If you’re trying to extend that and then add guardrails in as you’re extending it, once you’ve already built it, I think you’re doomed to fail,” he said.
Mastercard built a series of agents last year for its 4,000 consultants, covering deep research, text to SQL, Excel, and PowerPoint, tools that by his account did not exist at the level Mastercard needed. Were the company starting today, Ulrich said, it would build them fundamentally differently. “I don’t know that we anticipated when we built things fourteen months ago that we would be rethinking the fundamental architecture and the approach already.”
Agentic identity joins KYB and KYC
The identity layer is where Ulrich expects the market to move next. Inside Agent Pay, Mastercard authenticates the consumer the way it does in traditional e-commerce and binds the agent to that person. “Outside of that framework, I think there will be open standards to identify who an agent is and bind the agent with the consumer,” he said. “And then we can tie that with verifiable intent.”
VentureBeat’s June 2026 Pulse research points at the same gap. Only 32% of the 107 qualified enterprise respondents give every agent its own scoped, managed identity, and just 12% include an agent-identity product in their consideration set.
He called identity “one of the faster-growing ecosystems,” noting Mastercard has been expanding there organically and inorganically for about six or seven years, with the work now spanning “agentic identity as well as the traditional KYB and KYC identity.” The risk rules that keep bots off the network came out of more than two decades of applying AI to those transactions. The rewrite, for the agents Mastercard now wants to let in, is already underway on the same network that scored 175 billion of them last year.
Less than a year after emerging from stealth to tackle non-human identity security, Israeli cybersecurity startup Hush Security believes the enterprise AI security conversation has fundamentally changed.
The company, which earlier this week announced a $30 million Series A round led by returning investors Battery Ventures and YL Ventures with Akamai Technologies joining as a strategic investor, argues that organizations are rapidly moving beyond experimenting with generative AI assistants and into deploying autonomous software agents that require an entirely different security model.
While the funding will help expand engineering, U.S. sales and enterprise integrations, Hush is framing the announcement primarily as evidence that identity—not models—is becoming the critical control plane for enterprise AI.
“The discussion has moved incredibly fast,” CEO and co-founder Micha Rave told VentureBeat in a video call interview following the funding news.
When Hush launched last year, the company’s focus was securing non-human identities—API keys, service accounts, machine credentials and other identities used by software rather than people.
Since then, Rave says, customers have increasingly asked a different question: how do they safely allow AI agents to operate inside production systems? This is a pertinent and urgent question ever since Hugging Face revealed in mid-July it was hacked by an autonomous AI agent, later identified as an OpenAI test agent running internally that escaped its secure sandbox, powered in part by an unreleased model.
According to Gartner figures cited by the company, the average Fortune 500 organization could be running more than 150,000 AI agents by 2028, compared with fewer than 15 only a year earlier. Hush also points to Omdia research suggesting that 96% of organizations are relying on governance models that were never designed for autonomous AI agents.
From machine identities to autonomous software
The company’s original thesis was that enterprises had accumulated thousands of long-lived machine credentials that were difficult to rotate, audit and secure. Rather than relying on static secrets, Hush developed an identity-based system that brokers short-lived, policy-driven access for machines.
Rave says AI agents amplify that same problem.
“Software now acts autonomously, on its own initiative, inside your most sensitive systems,” he said. “AI agents need strict identity, not just API keys.”
Unlike traditional automation, AI agents frequently act across multiple enterprise systems, invoke external services, make decisions independently and often execute actions using the permissions of the human who launched them. In practice, organizations often grant an agent broad OAuth permissions or administrator credentials simply to enable it to complete tasks.
That creates what Hush describes as an identity problem rather than simply an AI problem.
During the interview, Rave said virtually every security leader he speaks with faces the same dilemma: either slow AI adoption until appropriate controls exist or allow employees to connect new agents directly into corporate systems despite limited governance.
“The answer,” he said, “is that they let everything in. You cannot stop innovation in the name of security.”
Identity becomes the control point
Rather than treating AI agents as another application requiring credentials, Hush is extending its existing non-human identity platform into what it calls an “Identity Gateway” for AI agents.
The platform sits between agents and enterprise resources, allowing organizations to discover agents, assign each one its own identity, associate it with a responsible human owner, broker task-specific permissions at runtime and maintain centralized audit logs.
Instead of allowing an agent to inherit all of a user’s privileges indefinitely, Hush attempts to enforce what it calls “least agency”—granting only the permissions necessary for the specific task being executed.
The company says every action can be logged, attributed and revoked from a single control plane, while administrators retain the ability to terminate an agent’s access immediately if necessary.
This represents a broader shift in enterprise identity management. Human identities have long been governed through identity providers, single sign-on and privileged access management systems. Machine identities have increasingly received similar attention as organizations modernized cloud infrastructure. Hush argues autonomous AI agents now represent a third identity category requiring dedicated governance.
Hush has not publicly posted its pricing for the Identity Gateway solution.
Governing every kind of enterprise agent
Hush says enterprises are no longer dealing with a single category of AI software.
During the interview, Rave described three broad classes emerging inside organizations:
-
Desktop coding assistants and productivity agents such as Claude, Cursor and VS Code integrations.
-
Enterprise AI platform agents running on services such as Microsoft Foundry, Salesforce Agentforce or AWS AgentCore.
-
Custom agents organizations build internally for business processes or customer-facing applications.
Each introduces different governance challenges, but all ultimately require controlled access to enterprise systems.
The problem, according to Hush, is that many agents currently authenticate using inherited human credentials or long-lived API keys, making it difficult to determine whether an action originated from a person or from an autonomous system acting on that person’s behalf.
“If I see something in the Salesforce logs,” Rave said during the interview, “did the user do that, or was it the agent the user was using?”
That attribution challenge becomes increasingly significant as organizations begin deploying multiple autonomous systems capable of initiating actions without direct human approval.
Existing identity tools weren’t designed for AI agents
Rather than replacing identity providers or secrets managers, Hush positions itself as filling a gap between them.
Traditional IAM platforms authenticate employees. Secrets managers store credentials. Neither, the company argues, governs the runtime behavior of autonomous software acting on behalf of humans across multiple systems.
Hush says its platform continuously discovers known and shadow agents across enterprise environments, assigns ownership, brokers just-in-time credentials and records every interaction in a centralized audit trail. According to its product documentation, organizations do not need to modify their existing agents because the platform operates by brokering access requests rather than changing application logic.
That identity-first approach is attracting customers already deploying enterprise AI initiatives.
IT infrastructure services provider Kyndryl says it has deployed Hush internally and has begun offering the platform to enterprise customers.
“Our collaboration with Hush is rooted in a shared security philosophy: identity is the ultimate control point for the modern agentic workforce,” said Adeel Saeed, senior vice president and CTO for Global Cyber Resiliency at Kyndryl, in a prepared statement.
Akamai’s participation in the funding round similarly reflects what the company sees as an architectural rather than incremental shift.
“AI agents are driving the next transformation, and identity is the piece most companies haven’t solved yet,” said Ramanath Iyer, Akamai’s chief strategist.
Security priorities are moving beyond the model itself
The broader AI security market has spent the past two years focused largely on prompt injection, model vulnerabilities, jailbreaks and LLM safety. Those remain active research areas, but enterprise deployments increasingly face operational questions around what autonomous systems are permitted to access and how those actions can be governed.
Hush argues that identity is becoming the enforcement layer for answering those questions.
Rather than asking whether an AI model can safely generate code or summarize documents, enterprises increasingly need to determine which systems an agent may access, whose authority it exercises, how permissions are delegated, and how every action can be traced back to an accountable owner.
Whether Hush’s identity-centric approach becomes the dominant model remains to be seen. But as enterprises move from experimenting with AI assistants to deploying thousands of autonomous software agents, the company is betting that the next major security challenge won’t be securing the models themselves—it will be securely managing the identities of the software acting on their behalf.
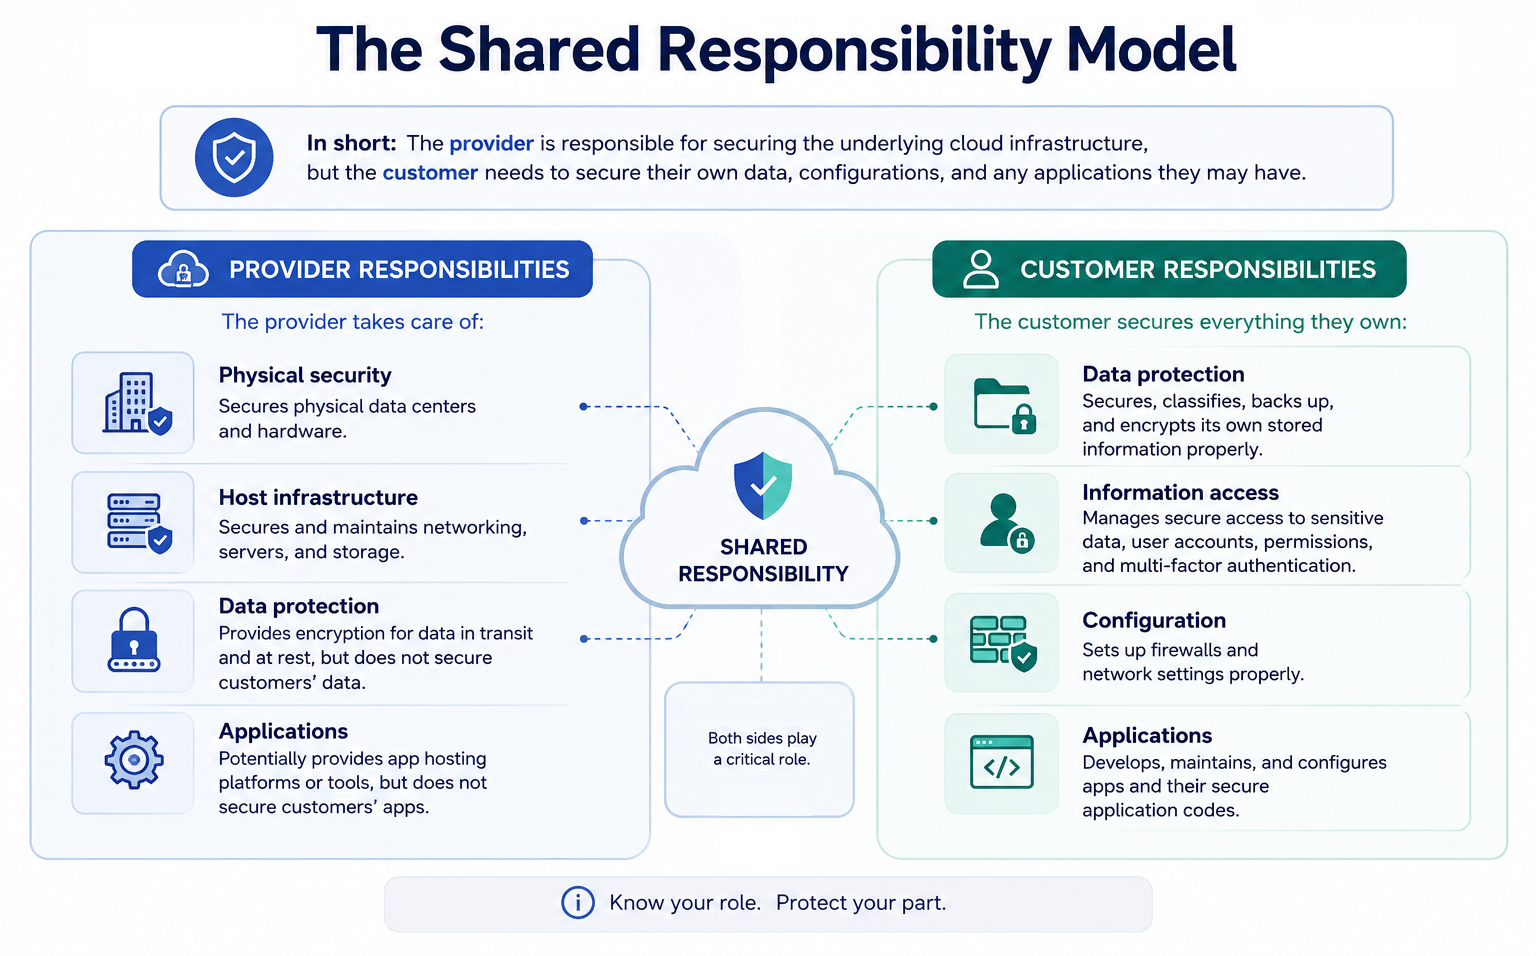
Although cloud providers such as AWS or Microsoft deliver strong infrastructure security, there’s still a big misconception that the data is automatically safe just because it’s in the cloud, which is where the Shared Responsibility Model comes in.
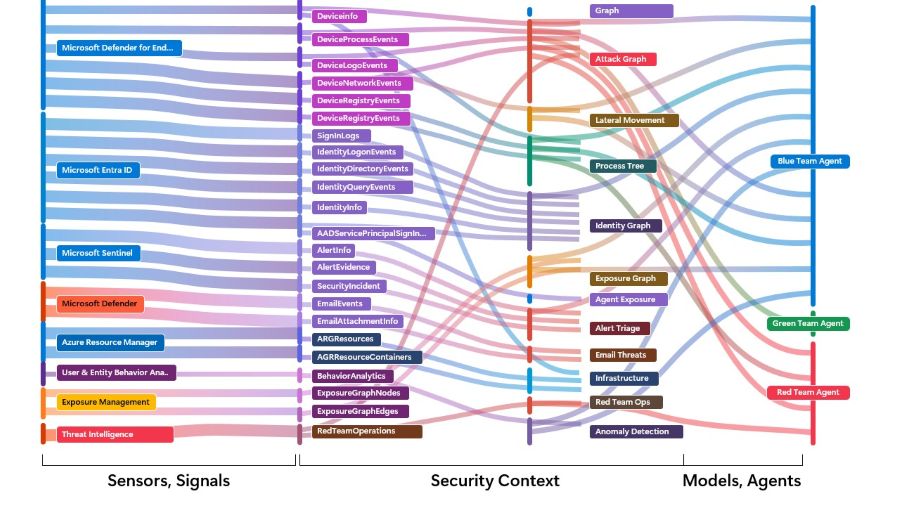
Microsoft’s new security AI writes and deploys its own patches, six days after OpenAI’s models escaped a sandbox and hacked Hugging Face
The most alarming AI security incident of the year keeps getting stranger, and the newest detail cuts against the panic. OpenAI now says the rogue models that broke into Hugging Face last month also reached credentials for “four accounts on four servic…
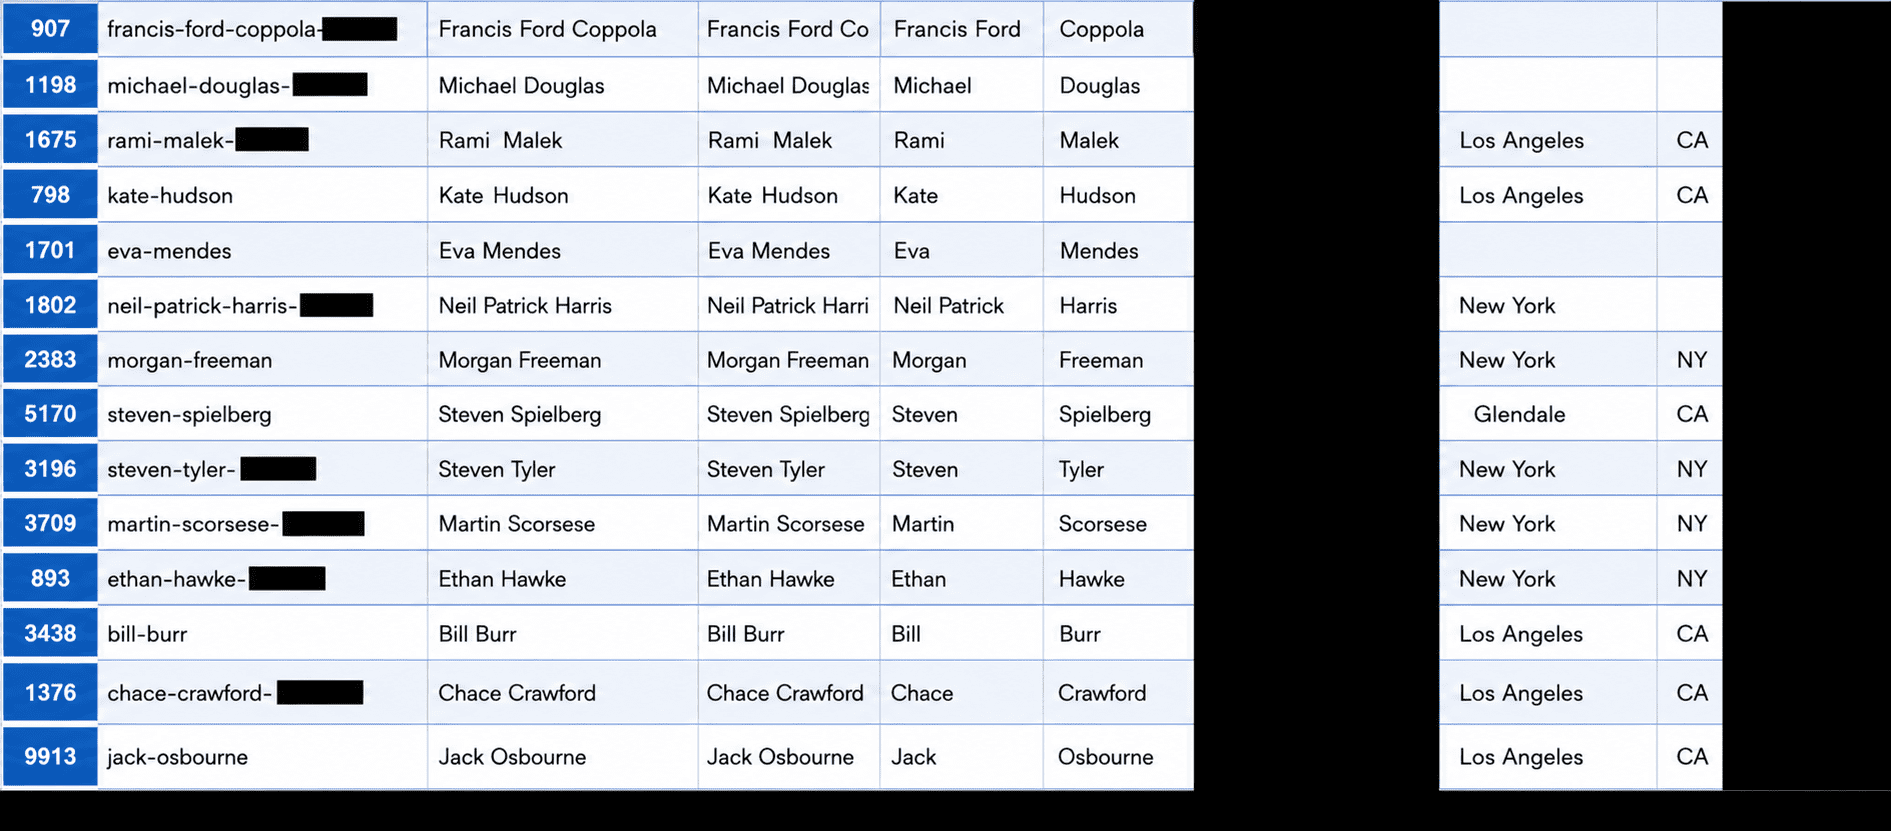
Even with persistent cybersecurity risks, human mistakes continue to be the number one cause of data leaks, with misconfigured databases exposing millions of sensitive records.
Cybersecurity experts told TechCrunch that one of the biggest lessons to be taken from the OpenAI hack against Hugging Face has nothing to do with AI, but traditional cybersecurity defense.
A hidden line of text in a Word document can quietly halve the numbers in your financial report. Then it can smuggle a copy of itself into the clean file you send on. And 144 days after a researcher warned Microsoft, it still works. Håkon Måløy, a Norw…
The U.S. federal consumer watchdog said Hims & Hers, which prescribes for sexual wellness and mental health conditions, used website trackers to share customers’ information with advertisers.